Safety structure in hybrid environments has historically targeted on well-known ideas reminiscent of OWASP vulnerabilities, id and entry administration, role-based entry management, community safety, and the precept of least privilege. Greatest practices like safe coding and incorporating SAST/DAST testing into CI/CD pipelines are additionally broadly mentioned.
Nevertheless, when organizations function in a hybrid mannequin — operating workloads each on-premises and within the cloud — whereas additionally integrating with vendor-managed cloud options, a special set of safety design issues comes into play. These situations are usually not unusual, but they’re not often highlighted within the context of safe answer implementation involving vendor software program in hybrid environments.
This text highlights 4 real-world use circumstances and descriptions sensible architectural methods for organizations to undertake to make sure safe integration in hybrid settings.
Acronyms
- OWASP – Open Internet Software Safety Undertaking
- SAST – Static Software Safety Testing
- DAST – Dynamic Software Safety Testing
- CI/CD – Steady Integration / Steady Testing
- SaaS – Software program as a Service
- UX – Person Expertise
- ETL – Extract, Rework, and Load
Use Circumstances
There are three use circumstances this text covers, as listed under.
- Automated software program replace by the seller within the group’s managed knowledge middle
- Webhook – mismatch in verification methodology
- JavaScript embedding – monitoring mandate
Tactical Options
Automated Software program Replace by Vendor in Group-Managed Knowledge Heart
Downside Assertion
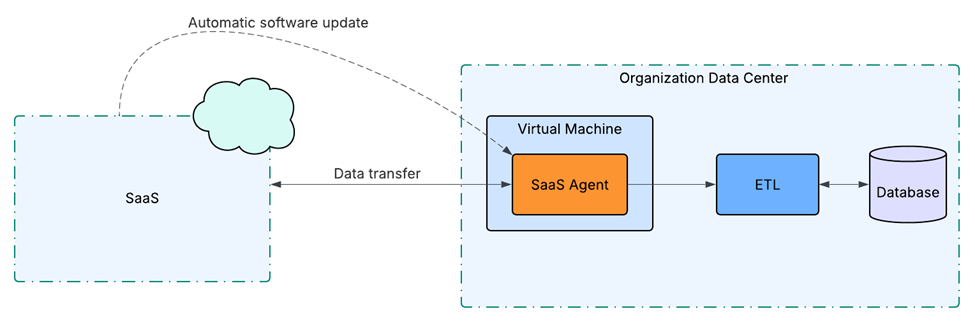
In some vendor software program integrations, organizations are required to put in an agent inside their very own knowledge middle. This agent usually acts as a bridge between the seller’s cloud-hosted utility and the group’s on-premises programs. For instance, it could facilitate knowledge switch between the seller software program and the group’s on-premises database.
In lots of circumstances, the seller’s operational structure requires that this agent be robotically up to date. Whereas handy, this method introduces a major safety danger. If the seller’s software program is compromised or incorporates malware, the replace course of may infect the digital machine or container internet hosting the agent. From there, the risk may propagate into different elements of the group’s infrastructure, probably resulting in a significant safety incident. Determine 1 showcases the situation.
Answer
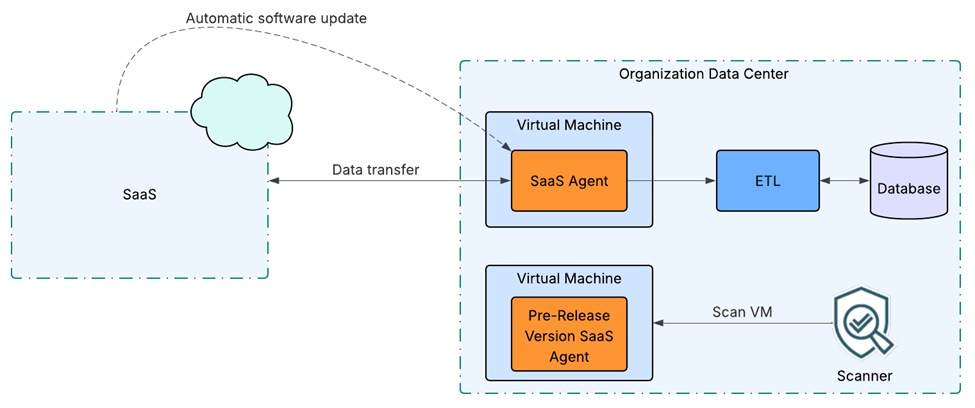
A tactical approach to remedy this downside is to put in the long run model of the agent software program in a separate digital machine or container and scan the software program in addition to the machine for any vulnerabilities. If the software program and the deployment platform the place the software program is operating move all the safety checks, then the seller could be permitted to put in the brand new model of the agent software program robotically. This manner it may be ensured that an unverified model of the seller software program doesn’t robotically get pushed to the group’s knowledge middle. Determine 2 demonstrates the answer.
Webhook: Mismatch in Verification Methodology
Downside Assertion
That is an fascinating safety situation the place we frequently stumble. For a webhook implementation, the group has to open up an inbound connectivity from the seller software program over the web. As it’s an inbound visitors to the group’s knowledge middle (on-prem or cloud), the inbound visitors must be verified from each facet of software program safety, reminiscent of DDoS assault, malicious payload, and so forth. Organizations typically have a well-defined frequent safety coverage to confirm all incoming visitors from exterior distributors.
Alternatively, vendor software program may additionally have a typical coverage that works as a tenet for his or her clients to confirm all facets of safety after they obtain inbound visitors from the seller webhook. It’s extremely unlikely that the safety coverage of a company and a vendor will match, particularly when each group and vendor are main gamers within the trade. Because the safety coverage doesn’t match the vast majority of the time, it creates a problem to implement such webhook integration.
Answer
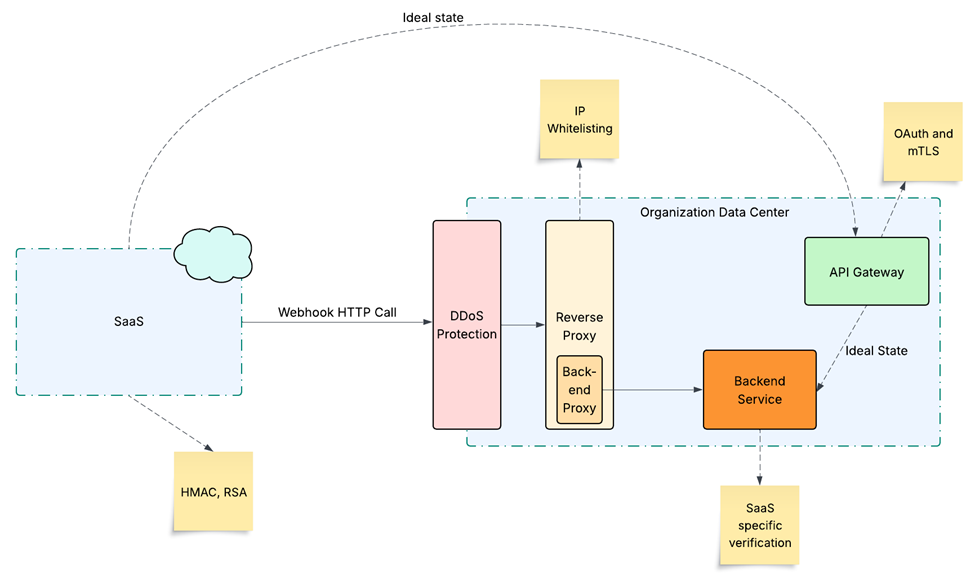
A tactical approach to remedy the problem is to let the incoming visitors hit a reverse proxy layer of the group. The reverse proxy layer, which receives visitors from the web, is mostly protected by a DDoS safety layer. The reverse proxy layer can ahead the incoming visitors to the backend service layer, which has the enterprise logic to course of the webhook request. The backend service layer can implement the payload and different verification of the seller webhook incoming visitors based mostly on the coverage arrange for the seller specification. Determine 3 demonstrates the tactical answer.
JavaScript Embedding: Monitoring Mandate
Downside Assertion
Among the vendor options lately are JavaScript toolkits. They’re usually Digital Adoption Platform (DAP) software program which are used to navigate customers by means of the UX of the net platform to make them accustomed to the navigation of newly launched options. The combination course of typically requires embedding the seller’s JavaScript toolkit throughout the group’s codebase. That is deemed dangerous because of script injection and different varieties of JavaScript vulnerabilities.
Along with that, vendor software program typically additionally has a characteristic to ship info from an internet browser to their system to seize knowledge for analytical functions. This analytical knowledge seize characteristic provides additional danger since there’s a chance of vendor software program capturing unauthorized knowledge parts about clients and functions of their system. The group, subsequently, prefers analytics visitors to circulate to the seller platform from the browser by means of its infrastructure. If the information flows by means of the group’s infrastructure, then the information that flows by means of the seller platform could be monitored and actioned upon as needed.
Answer
There are two issues to unravel on this use case:
- Safely combine the JavaScript package deal of the seller into the group’s codebase
- Implement an answer to ship analytics visitors from the browser to the seller by means of the group’s infrastructure
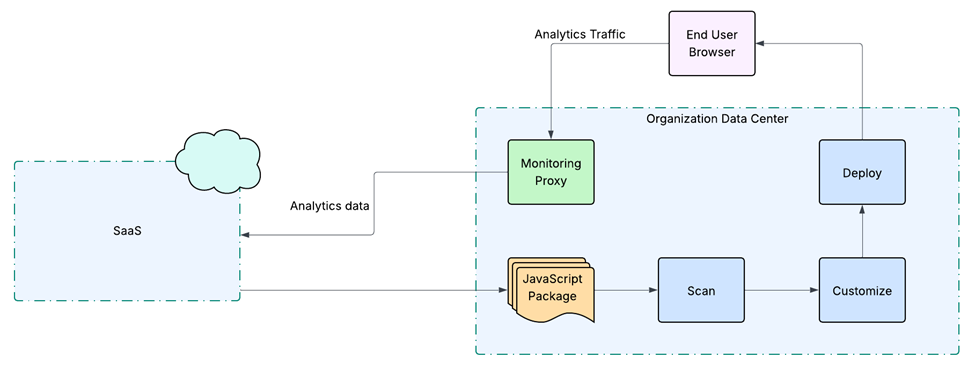
To implement a safe integration answer with the seller JavaScript software, the script must be packaged as a part of the CI/CD pipeline to scan and carry out SAST/DAST testing earlier than deploying. In an effort to route the analytics visitors to the seller platform by means of the group’s infrastructure, create a proxy to the goal vendor endpoint and customise the seller JavaScript to level to the proxy. This association helps in routing analytics visitors from the browser to the seller by means of the group’s infrastructure.
Conclusion
This text explored three real-world situations that spotlight the safety challenges organizations face when integrating vendor software program into hybrid environments. Every use case demonstrates how seemingly routine technical choices — reminiscent of software program updates, webhook validation, or JavaScript embedding — can introduce vulnerabilities if not fastidiously addressed. The options offered are usually not simply theoretical greatest practices however tactical architectural selections that organizations can undertake to implement options in a safe approach for these much less talked about however frequent integration challenges.