A gaggle of China-linked hackers referred to as Mustang Panda has expanded its spying efforts to focus on the Indian monetary sector and political circles in South Korea. The Acronis Menace Analysis Unit found the group’s newest exercise after its earlier marketing campaign involving Venezuela-related lures designed to focus on US authorities earlier in 2026.
Concentrating on HDFC Financial institution and Diplomacy Consultants
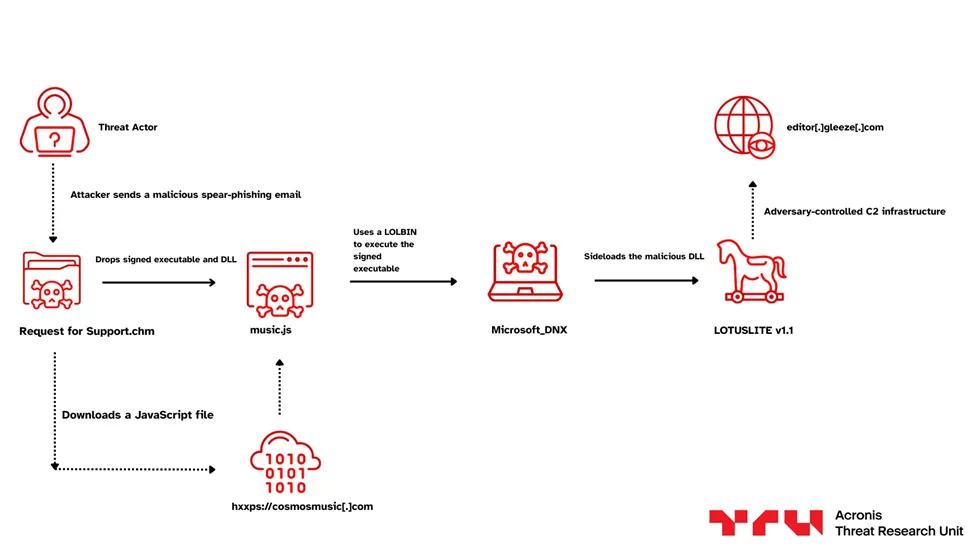
The hackers reportedly started this dual-sided marketing campaign in March 2026. In India, they used a file named Request for Assist.chm to trick staff within the banking sector. This file contained a pop-up window that talked about HDFC Financial institution Restricted to look official, and when a consumer clicked the file, it triggered a series of occasions that concerned downloading a malicious JavaScript file known as music.js from the area cosmosmusiccom.
Acronis’ investigation, shared with Hackread.com, revealed that the hackers didn’t cease at help tickets. They even made faux pop-up home windows that regarded like actual HDFC Financial institution software program. Whereas the employees thought they have been taking a look at a banking app, a brand new model of the LOTUSLITE backdoor, known as LOTUSLITE v1.1, was truly spying on the system.
In one other a part of the marketing campaign, the group pretended to be Victor Cha, a former Director for Asian Affairs on the US Nationwide Safety Council. Utilizing a faux Gmail account ([email protected]) with Mr Cha’s actual picture, they despatched out Google Drive hyperlinks to folders named March 30. Inside have been faux invitation letters crafted to contaminate the computer systems of policy-makers.
Identical Tips, New Names
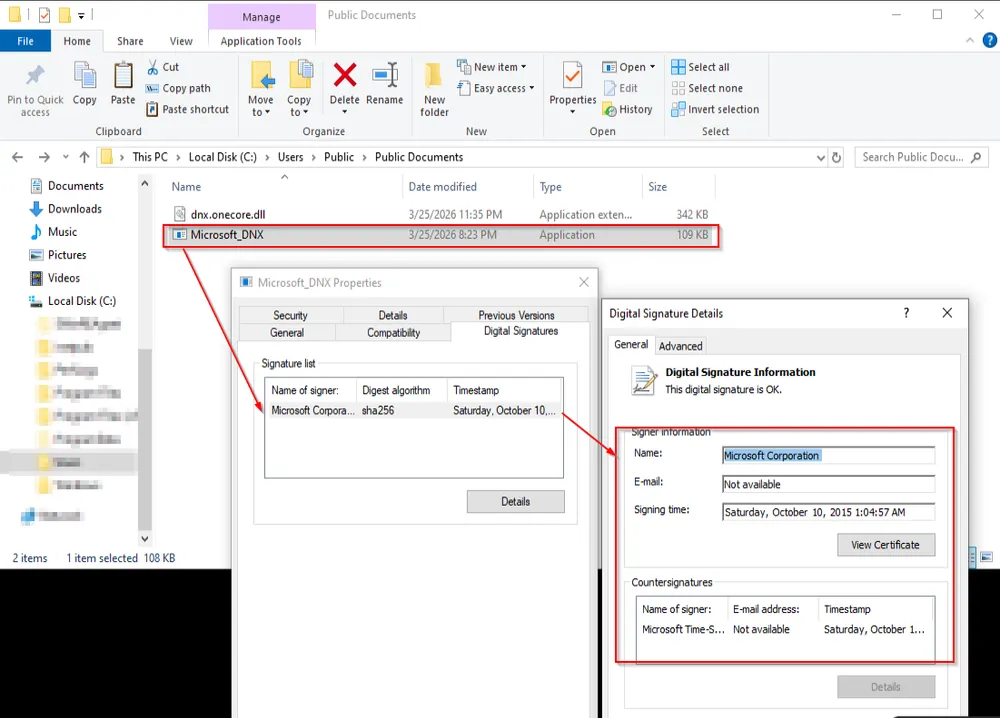
The hackers are utilizing a technique known as DLL sideloading. They mainly take a protected file signed by Microsoft (like Microsoft_DNX.exe) and put their very own malicious file proper subsequent to it. The pc trusts the Microsoft title, so it lets that contaminated file run with out a second thought.
In line with researchers, the group is attempting to cover higher. They rotated the interior code marker or ‘magic worth,’ a selected code used to establish their site visitors, from 0x8899AABB to 0xB2EBCFDF, and likewise changed a command flag named –DATA with a brand new one known as –ZoneMAX.
Researchers additionally famous that the hackers used a service known as Gleeze to speak with their server at editorgleezecom. This is identical infrastructure utilized in earlier assaults, which helped consultants hyperlink the exercise to Mustang Panda.
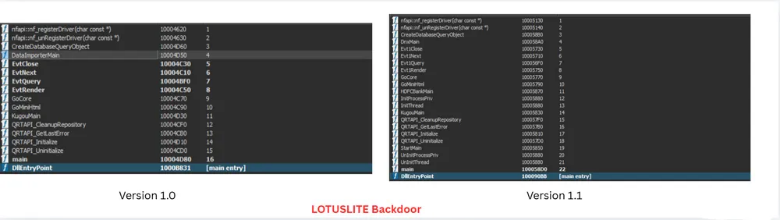
Regardless that the group tried to replace their strategies, they left behind previous code names like KugouMain and DataImporterMain within the new information. They even left a message within the code mentioning a safety researcher who has been monitoring them.
Nonetheless, they’re consistently upgrading their impersonating experience and utilizing trusted software program to lure customers, which makes it important for everybody to remain sceptical of any sudden emails or information, even when they give the impression of being official.