MacSync Stealer is increasing its macOS-focused theft operation via a rotating community of greater than 30 domains, utilizing secure execution and community patterns to steal credentials, browser knowledge, cloud entry keys, SSH materials, and delicate person information.
Earlier analysis by RST Cloud recognized MacSync infrastructure and noticed command-and-control substitute after public disclosure.
Microsoft’s subsequent telemetry-led investigation linked the broader marketing campaign by correlating endpoint and community proof throughout payload supply, beaconing, assortment, staging, and lively exfiltration.
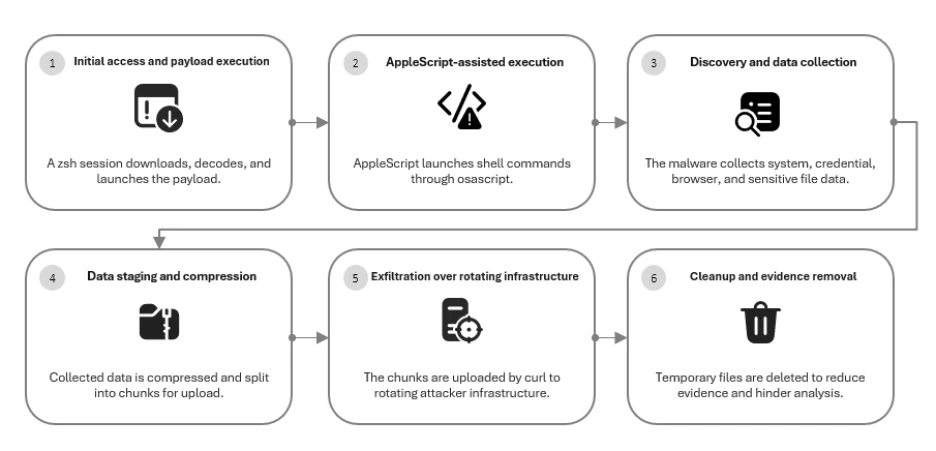
Preliminary execution generally begins with a ClickFix-style social-engineering lure. Victims are persuaded to stick a command into Terminal, launching an interactive zsh shell that makes use of curl to fetch attacker-controlled content material from paths resembling /curl/[token].
The downloaded payload is then decoded or unpacked utilizing native utilities, together with Base64 and gunzip, earlier than script-driven execution begins.
The malware additionally abuses osascript to bridge AppleScript and shell instructions, enabling execution of utilities corresponding to sh, cp, rm, mkdir, curl, and killall.
This mix is critical for defenders as a result of AppleScript spawning shell exercise adopted by community entry, temporary-file staging, or cleanup is a extra dependable behavioral sign than a single malicious area.
As soon as lively, MacSync Stealer profiles the machine and searches for high-value knowledge.
Microsoft Defender Specialists discovered that whereas the infrastructure modifications quickly, the malware’s recurring curl instructions, URI paths, headers, staging conduct, and chunked uploads provide defenders sturdy detection alternatives.
MacSync Stealer Makes use of 30+ Rotating Domains
Microsoft noticed assortment focusing on macOS Keychain materials, browser Secure Storage keys, cookies, credentials, login databases, session knowledge, IndexedDB and LevelDB shops, extension knowledge, Safari artifacts, Apple Notes, searching historical past, SSH keys, AWS credentials, Kubernetes configuration information, and information in frequent person directories.
The stealer additionally checks for cryptocurrency wallet-related artifacts related to Ledger and Trezor functions.
Quite than merely speaking with C2 servers, the malware phases stolen materials beneath paths matching /tmp/sync*, compresses it into /tmp/osalogging.zip, then splits the archive into chunks for switch.
Exfiltration makes use of curl with HTTP PUT requests and the --data-binary choice. Requests embrace recurring fields corresponding to upload_id, chunk_index, and total_chunks, alongside macOS Person-Agent strings and API-key headers.
These traits let defenders determine MacSync exercise even when operators abandon recognized domains.
Microsoft linked infrastructure via recurring paths together with /curl/, /dynamic?txd=, and /gate?buildtxd=; curl arguments corresponding to -k, -s, --max-time, and --data-binary; and the distinctive chunked-upload parameters.
RST Cloud equally recognized eleven candidate domains via URI conduct and reported a static API-key worth shared throughout 4 confirmed C2 domains, regardless of rotating construct tokens.
The marketing campaign illustrates why static IOC blocking alone is inadequate in opposition to fast-moving macOS malware operations.
Safety groups ought to correlate interactive Terminal or zsh periods with curl-based downloads, Base64 or gunzip unpacking, osascript-initiated shell exercise, delicate credential-store entry, archive creation in short-term directories, and subsequent outbound HTTP PUT visitors.
Organizations also needs to monitor for deletion of short-term archives, staging directories, and lock information instantly after add exercise, as MacSync makes an attempt to take away proof after theft.
Detection logic ought to prioritize the complete sequence: suspicious user-initiated shell execution, native utility abuse, assortment of credential and cloud artifacts, /tmp staging, archive compression, and chunked curl uploads.
Apple has added ClickFix-focused safeguards in macOS 26.4 and later, together with Terminal paste warnings supposed to dam probably malicious directions.
Apple’s XProtect protections may stop detected malicious scripts from operating.
Enterprises ought to pair these platform controls with cloud-delivered endpoint safety, net and community filtering, and tamper safety to scale back the prospect that customers can execute attacker-provided Terminal instructions.
IOCs
| fintelliganceai [.]com | Area | Associated MacSync Stealer infrastructure recognized via behavioral searching. |
| homeinspectionsdelaware [.]com | Area | Associated MacSync Stealer infrastructure recognized via behavioral searching. |
| intopython [.]com | Area | Associated MacSync Stealer infrastructure recognized via behavioral searching. |
| lalandscapelighting [.]com | Area | Associated MacSync Stealer infrastructure recognized via behavioral searching. |
| lumenagnet [.]com | Area | Associated MacSync Stealer infrastructure recognized via behavioral searching. |
Be aware: IP addresses and domains are deliberately defanged (e.g., [.]) to stop unintentional decision or hyperlinking. Re-fang solely inside managed menace intelligence platforms corresponding to MISP, VirusTotal, or your SIEM.
★ Which Safety Instruments Ought to You Lower? Rating Them on One Web page – Obtain the Inherited Safety Stack Information