Staff connecting to resort or convention Wi-Fi are being focused via the community gear managing their connection, permitting attackers to redirect them to faux Microsoft login pages with out sending a phishing e mail or infecting their computer systems.
The marketing campaign has operated since at the least June 2026, in accordance with analysis printed by ReliaQuest, which recognized compromised Wi-Fi gateways in a number of US cities, India, and Saudi Arabia, with connections involving workers from finance, authorized, well being care, power, retail, {and professional} companies organizations.
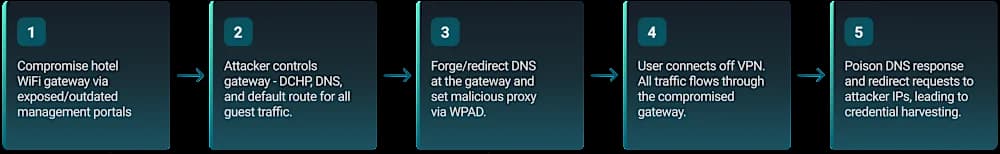
For context, a resort visitor can be part of the venue’s real Wi-Fi community and nonetheless be uncovered. As soon as attackers receive administrative entry to its gateway, they will alter the system that directs web visitors for each related visitor.
Compromised Wi-Fi Redirects Microsoft Logins
When a tool requests a web site, DNS converts its title into the numerical handle wanted to succeed in it. A compromised gateway can present a false reply, sending the browser to infrastructure operated by the attacker.
ReliaQuest noticed Microsoft-themed domains reminiscent of m365-owa.com, owa-ms365.com, ms365-device.com and ms365-live.com. These weren’t Microsoft companies, however names designed to resemble official Microsoft 365 and Outlook addresses.
In line with ReliaQuest’s weblog put up, vacationers redirected to these pages could possibly be requested to enter their login particulars. In a restricted variety of instances, the attackers additionally abused Microsoft’s device-code authentication course of. A sufferer approving the request might give the attacker legitimate entry tokens, even when multifactor authentication was accomplished on a real Microsoft web page.
The researchers consider the gateways could have been compromised via internet-facing administration companies mixed with weak or reused administrator passwords. Nonetheless, restricted entry to the affected gadgets prevented them from confirming the preliminary entry technique.
Some affected gadgets additionally tried to make use of Home windows Net Proxy Auto-Discovery, often known as WPAD, to route software visitors via an attacker-controlled proxy. ReliaQuest noticed this exercise in roughly one-third of the examined instances however couldn’t affirm that it succeeded.
Strategies Resemble Earlier APT28 Campaigns
ReliaQuest discovered similarities between this operation and earlier router assaults related to APT28, additionally known as Fancy Bear and Forest Blizzard. The Russian army intelligence group has beforehand been linked to DNS manipulation used to compromise Microsoft 365 accounts.
These similarities embody taking management of community gateways, altering DNS responses and directing Microsoft authentication visitors via an adversary-in-the-middle service. ReliaQuest didn’t immediately attribute the brand new marketing campaign to APT28 as a result of it discovered no shared infrastructure, reused code or different agency technical connection.
Moreover, researchers discovered a number of variations. As an example, the present operation targets resort and convention Wi-Fi gear, whereas earlier APT28 reporting targeted on residence and small-office routers. Its domains and IP addresses additionally differ from infrastructure beforehand related to the Russian group.
At all times-On VPN Stops the Wi-Fi Redirect
ReliaQuest says an always-on, full-tunnel VPN can cease this assault by sending web visitors and DNS requests via the corporate community. The resort gateway can not redirect the worker to a faux login web page as a result of the VPN handles these requests first.
This safety must activate as quickly because the system connects. A VPN that workers begin manually could go away a brief interval when the resort community can intrude with visitors, whereas break up tunneling can go away DNS requests outdoors the protected connection.
The researchers additionally warn that merely altering the system to Google’s 8.8.8.8 DNS service will not be sufficient. Until the request is encrypted, it nonetheless travels via the compromised gateway, which might intercept it and return a false handle.
Nonetheless, workers ought to reject sudden Microsoft login or authorization requests on public Wi-Fi and inform their employer which venue and community they have been utilizing.