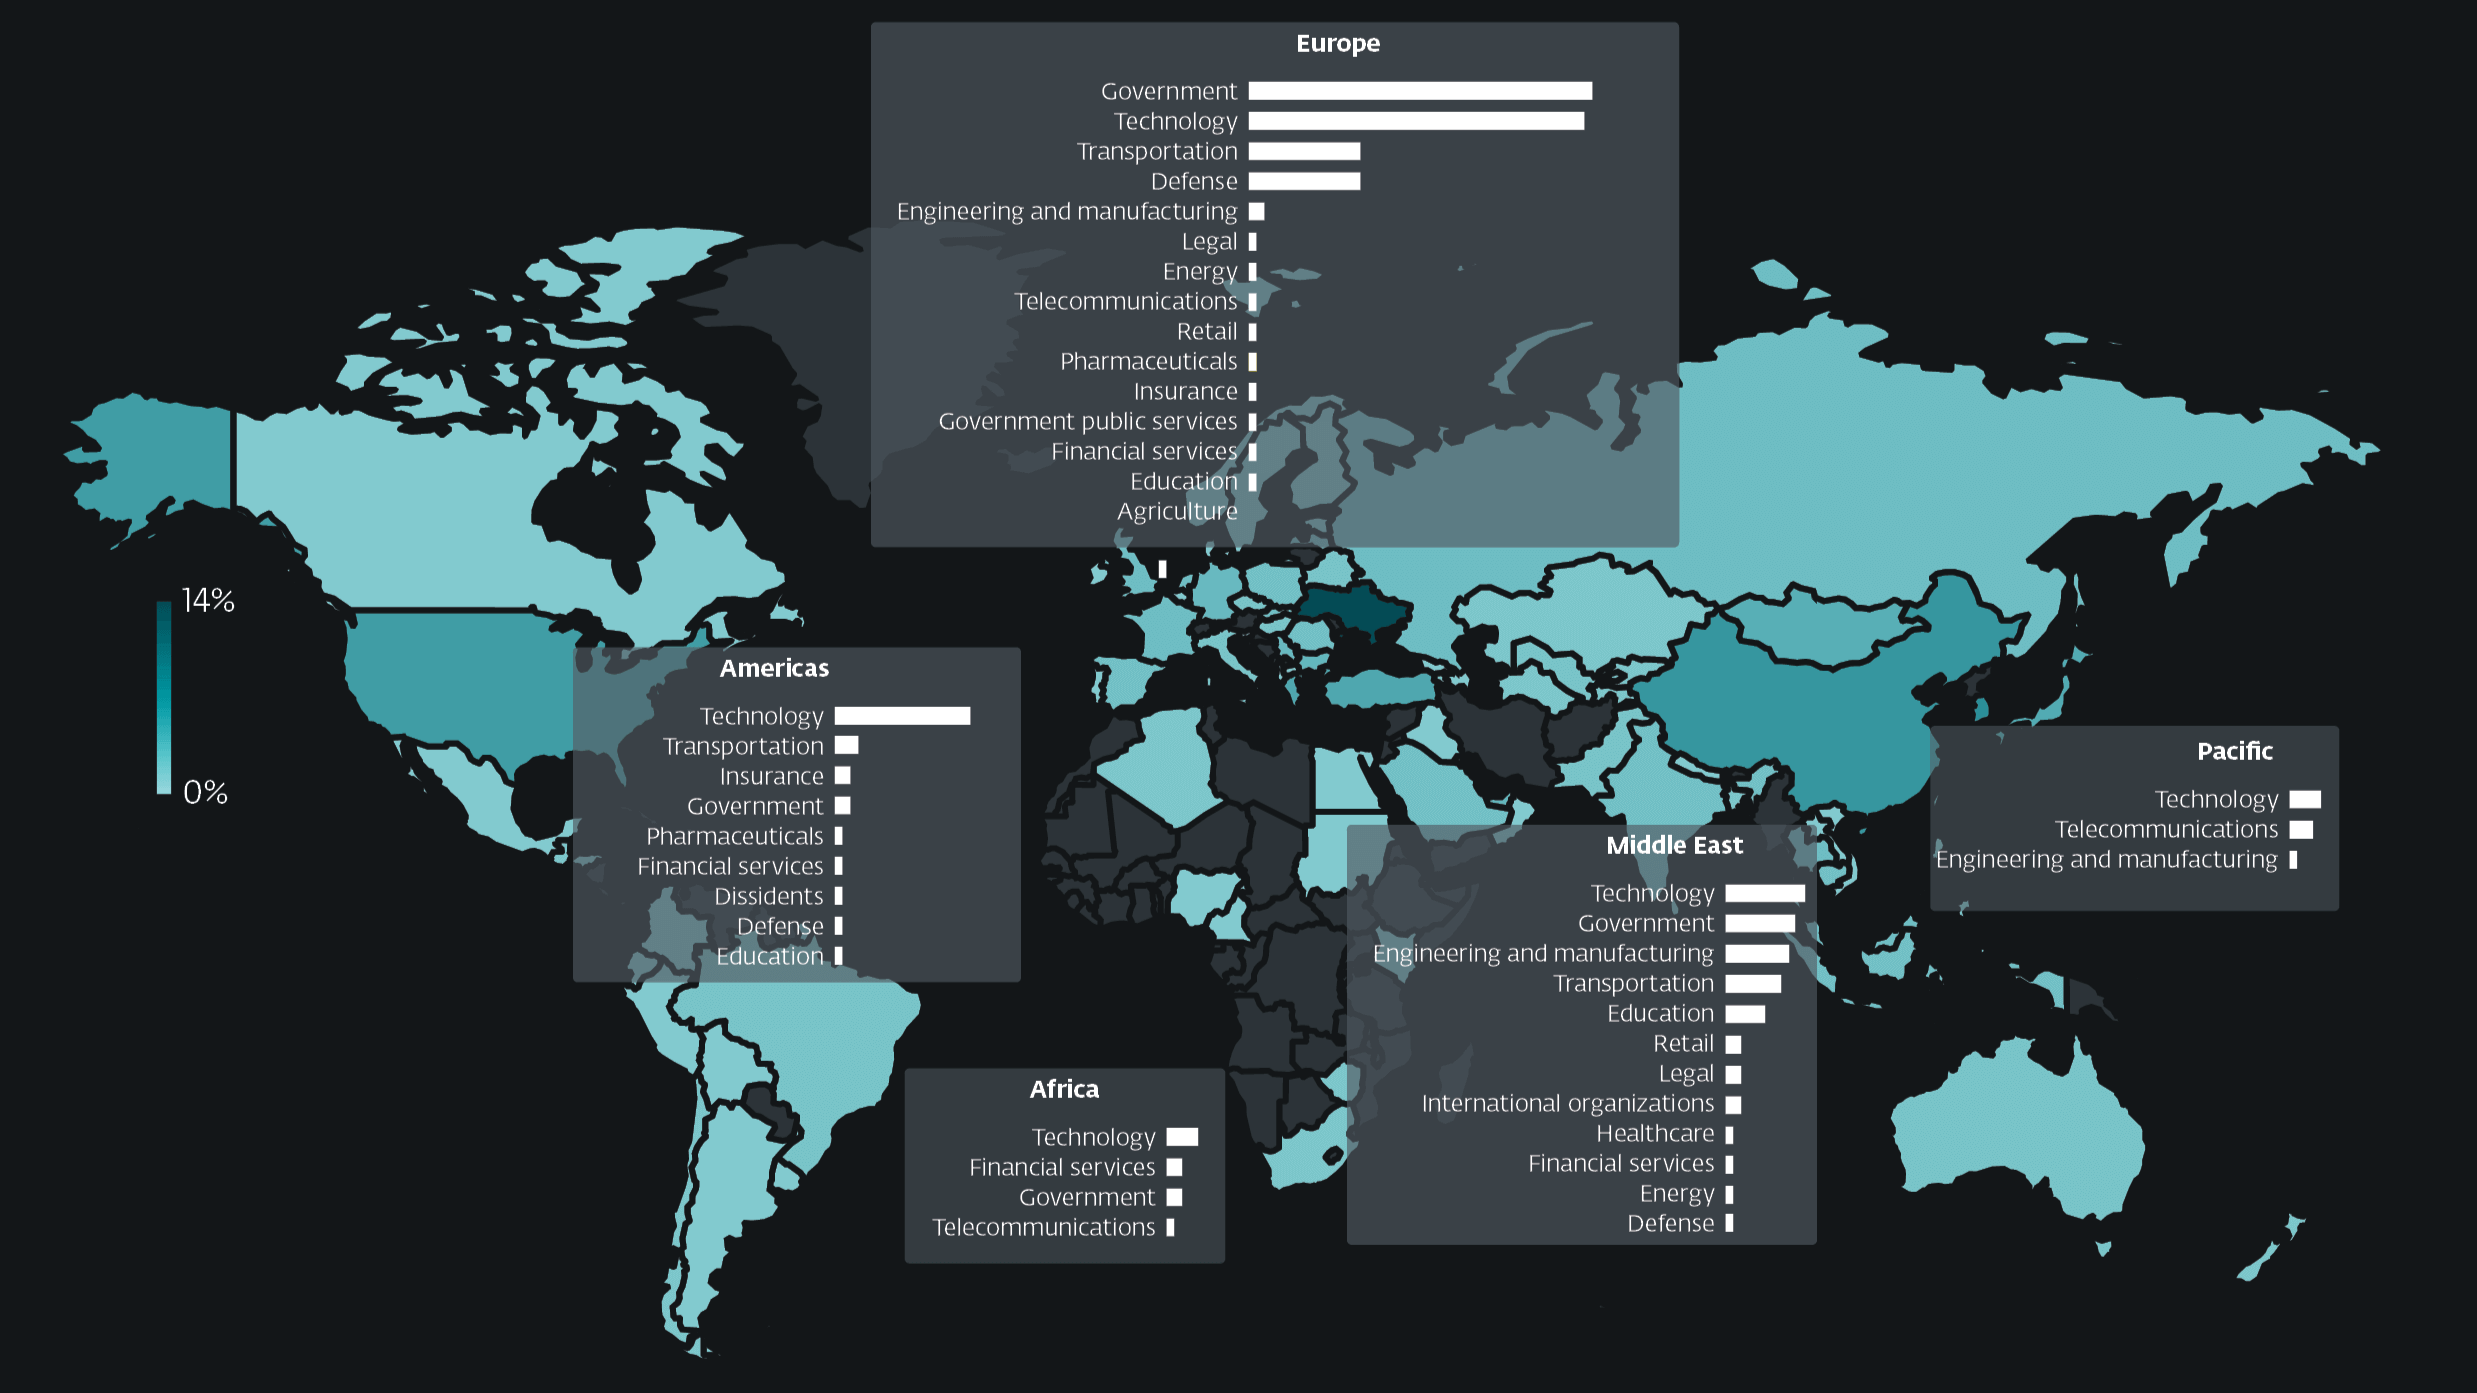
ESET APT Exercise Report This fall 2024–Q1 2025 summarizes notable actions of chosen superior persistent risk (APT) teams that had been documented by ESET researchers from October 2024 till the tip of March 2025. The highlighted operations are consultant of the broader panorama of threats we investigated throughout this era, illustrating the important thing developments and developments, and include solely a fraction of the cybersecurity intelligence information supplied to clients of ESET’s personal APT reviews.
Throughout the monitored interval, China-aligned risk actors continued partaking in persistent espionage campaigns with a concentrate on European organizations. Mustang Panda remained probably the most lively, focusing on governmental establishments and maritime transportation corporations through Korplug loaders and malicious USB drives. DigitalRecyclers continued focusing on EU governmental entities, using the KMA VPN anonymization community and deploying the RClient, HydroRShell, and GiftBox backdoors. PerplexedGoblin used its new espionage backdoor, which we named NanoSlate, towards a Central European authorities entity, whereas Webworm focused a Serbian authorities group utilizing SoftEther VPN, emphasizing the continued reputation of this instrument amongst China-aligned teams. Moreover, we consider {that a} ShadowPad cluster that will sporadically deploy ransomware for monetary acquire is primarily engaged in espionage. We additionally highlighted Worok’s frequent use of shared espionage toolsets equivalent to HDMan, PhantomNet, and Sonifake, addressing a number of inconsistent third-party attributions of campaigns involving these instruments to different teams.
Iran-aligned risk actors remained extremely lively, led by MuddyWater, which steadily leveraged distant monitoring and administration (RMM) software program in spearphishing assaults. Notably, MuddyWater collaborated intently with Lyceum, an OilRig subgroup, to focus on an Israeli manufacturing firm. BladedFeline revisited its earlier sufferer, a telecommunications firm in Uzbekistan, coinciding with Iran’s diplomatic outreach. CyberToufan performed damaging operations, deploying a wiper assault towards a number of organizations in Israel.
North Korea-aligned risk actors had been notably lively in financially motivated campaigns. DeceptiveDevelopment considerably broadened its focusing on, utilizing pretend job listings primarily inside the cryptocurrency, blockchain, and finance sectors. The group employed progressive social engineering methods, equivalent to ClickFix assaults and bogus GitHub concern posts, to distribute the multiplatform WeaselStore malware. The Bybit cryptocurrency theft, attributed by the FBI to TraderTraitor, concerned a supply-chain compromise of Secure{Pockets}, that brought on losses of roughly USD 1.5 billion. In the meantime, different North Korea-aligned teams noticed fluctuations of their operational tempo: In early 2025, Kimsuky and Konni returned to their typical exercise ranges after a noticeable decline on the finish of 2024, shifting their focusing on away from English-speaking suppose tanks, NGOs, and North Korea specialists to focus totally on South Korean entities and diplomatic personnel; and Andariel resurfaced, after a 12 months of inactivity, with a complicated assault towards a South Korean industrial software program firm.
Russia-aligned risk actors, notably Sednit and Gamaredon, maintained aggressive campaigns primarily focusing on Ukraine and EU international locations. Sednit refined its exploitation of cross-site scripting (XSS) vulnerabilities in webmail providers, increasing Operation RoundPress from Roundcube to incorporate Horde, MDaemon, and Zimbra. We found that the group efficiently leveraged a zero-day vulnerability in MDaemon E mail Server (CVE‑2024‑11182) towards Ukrainian corporations, whereas RomCom demonstrated superior capabilities by deploying zero-day exploits towards Mozilla Firefox (CVE‑2024‑9680) and Microsoft Home windows (CVE‑2024‑49039). All of those vulnerabilities had been reported by ESET researchers to respective distributors. Gamaredon remained probably the most prolific actor focusing on Ukraine, enhancing malware obfuscation and introducing PteroBox, a file stealer leveraging Dropbox, whereas the notorious Sandworm group intensified damaging operations towards Ukrainian power corporations, deploying a brand new wiper named ZEROLOT through Energetic Listing Group Coverage and using RMM instruments in early compromise phases.
Lastly, notable actions by lesser-known teams included APT‑C‑60 specializing in people in Japan who’re presumably linked to North Korea, and a extremely focused phishing marketing campaign, performed by an as but unidentified risk actor, impersonating the World Financial Discussion board and election web sites, aiming to acquire delicate data from Ukrainian officers and diplomats. As well as, StealthFalcon performed espionage targeted operations in Türkiye and Pakistan.
Malicious actions described in ESET APT Exercise Report This fall 2024–Q1 2025 are detected by ESET merchandise; shared intelligence is primarily based on proprietary ESET telemetry information and has been verified by ESET researchers.