Right here’s a quick dive into the murky waters of shape-shifting assaults that leverage devoted phishing kits to auto-generate personalized login pages on the fly

09 Might 2025
•
,
4 min. learn

Phishing stays a very cussed risk within the cybersecurity panorama. It sticks round partly as a result of although the dangerous guys are at all times after the identical prize – folks’s login credentials and different delicate info – they by no means stop to evolve and adapt their ways.
One approach that has gained traction in recent times is using dynamically generated phishing pages. Utilizing devoted phishing-as-a-service (PhaaS) toolkits, attackers can spin up authentic-looking phishing pages on the spot, all whereas customizing them for whoever they’re focusing on.
As a substitute of laboriously cloning a goal web site, even much less tech-savvy attackers can get the toolkits to do the heavy lifting for them – and in actual time and on a mass scale at that. One well-known instance of such a toolset, referred to as LogoKit, first made headlines in 2021 and apparently it hasn’t gone wherever since.
A special kettle of fish
So, how do these tips truly play out?
Considerably predictably, the lure usually begins with an e mail that’s aimed to create a way of urgency or curiosity – one thing designed to make you click on shortly with out pondering twice.
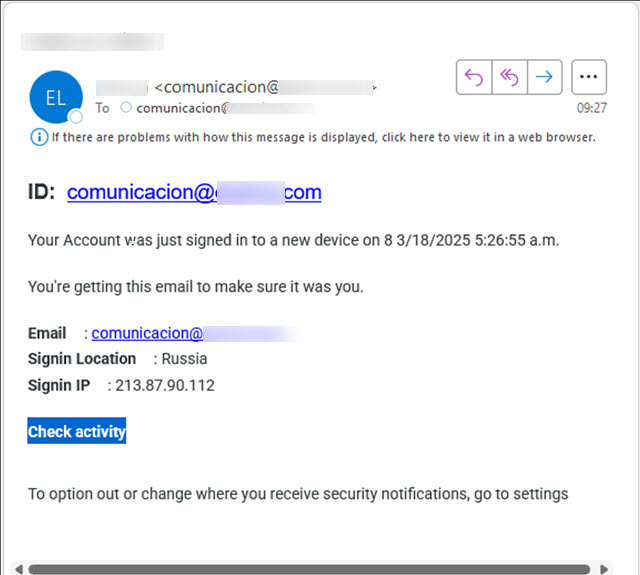
Clicking the hyperlink takes you to an internet site that may robotically retrieve the brand of the corporate that’s being impersonated, all whereas misusing the API (Software Programming Interface) of a official third-party advertising service reminiscent of Clearbit.
In different phrases, the credential-harvesting web page queries sources reminiscent of enterprise knowledge aggregators and easy favicon lookup providers to fetch the brand and different branding components of the corporate being impersonated, generally even including delicate visible cues or contextual particulars that additional enhance the ploy’s aura of authenticity.
Including to the deception, attackers may also pre-fill your title or e mail deal with, making it seem to be you’ve visited the positioning earlier than.
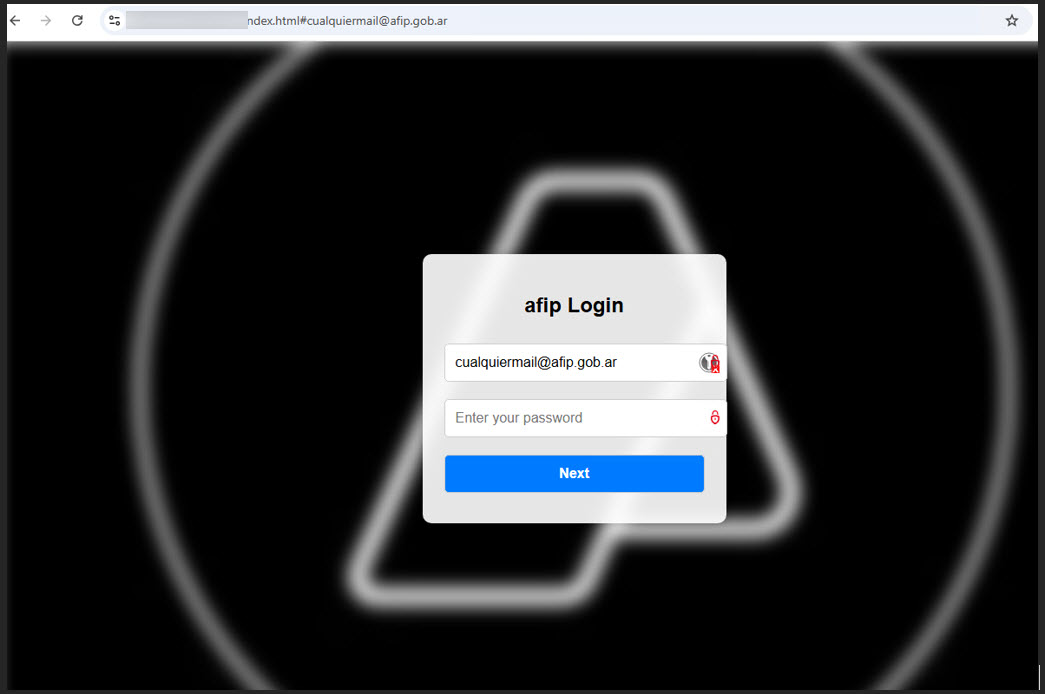
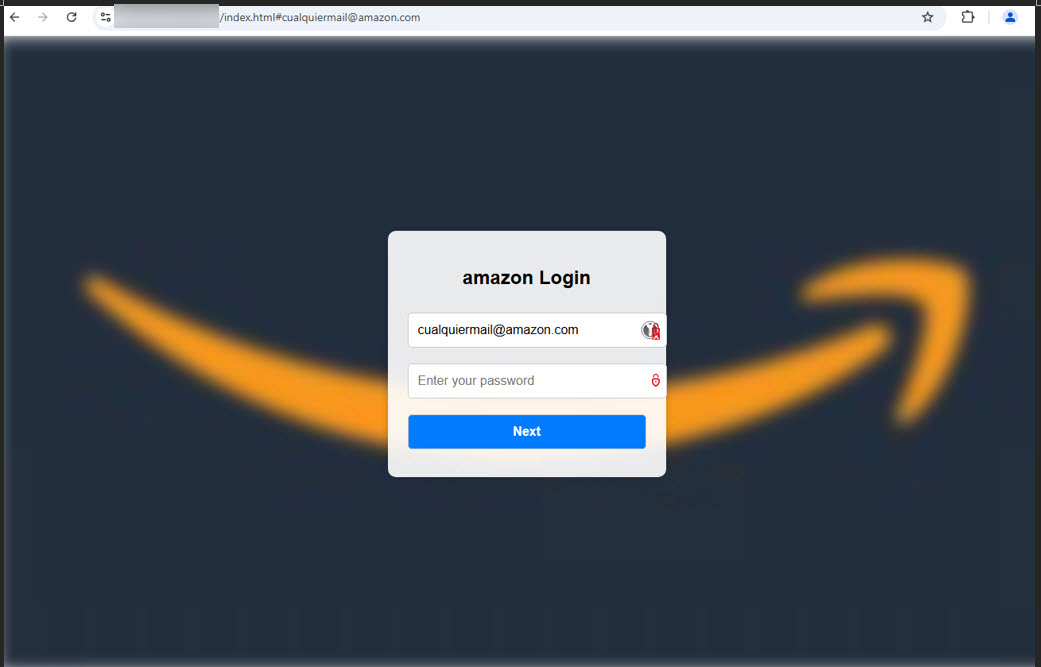
The login particulars are despatched in actual time to the attackers by way of an AJAX POST request. The web page ultimately redirects you to the precise official web site you meant to go to all alongside, leaving you none the wiser till it could be too late.
Loads of phish within the sea
It’s most likely apparent by now, however the approach is a boon for attackers for a number of causes:
- Actual-time customization: Attackers can tailor the web page’s look immediately for any goal, sourcing logos and different branding components from public providers on the fly.
- Enhanced evasion: Masking assaults with official visible components helps evade detection by many individuals and a few spam filters.
- Scalable and agile deployment: Assault infrastructure is usually light-weight and simply deployed on cloud platforms reminiscent of Firebase, Oracle Cloud, GitHub, and many others. This makes these campaigns simple to scale and more durable for defenders to establish and dismantle shortly.
- Lowered limitations to entry: Toolkits like LogoKit are available on underground boards, offering even much less tech-savvy people with the instruments wanted to launch assaults.
Staying off the hook
Defending towards evolving phishing ways requires a mix of ongoing private consciousness and strong technical controls. Nonetheless, just a few tried-and-true guidelines will go an extended approach to maintaining you secure.
If an e mail, textual content, or name asks you to click on a hyperlink, obtain a file, or present info, pause and confirm it independently. Don’t click on hyperlinks instantly in suspicious messages. As a substitute, navigate to the official web site or contact the group by means of a trusted, recognized cellphone quantity or e mail deal with.
Crucially, use a powerful and distinctive password or passphrase on all of your on-line accounts, particularly the dear ones. Complementing this with two-factor authentication (2FA) wherever obtainable can be a non-negotiable line of protection. 2FA provides a crucial second layer of safety that may stop attackers from accessing your accounts even when they handle to steal your password or supply it from knowledge leaks. Ideally, search for and use app-based or {hardware} token 2FA choices, that are usually safer than SMS codes.
Additionally, use strong, multi-layered safety options with superior anti-phishing protections on all of your gadgets.
The underside line
Whereas the purpose – stealing folks’s delicate info – is usually the identical, the ways utilized by cybercriminals are something however static. The form-shifting method proven above exemplifies the power of cybercriminals to repurpose even official applied sciences for nefarious ends.
The rise of AI-aided scams and different threats muddies the waters much more. With AI instruments within the palms of criminals, phishing emails can evolve past templated gibberish and turn into hyper-personalized. Combining vigilant consciousness with robust technical defenses will go a good distance towards maintaining the ever-morphing phish at bay..